

Exabeam
Exabeam was formed by merging with LogRhythm, a cybersecurity firm specializing in SIEM, log management, network monitoring, user behavior, and security analytics since 2002.
Exabeam is a global cybersecurity leader offering AI-powered security operations. High integrity data acquisition, powerful analytics, and workflow automation support the industry’s most advanced self-managing, cloud-based security operations platform for threat detection, investigation, and response (TDIR). With a history of leadership in SIEM and UEBA and a legacy of AI-driven solutions, Exabeam fully equips global security teams to combat cyber threats, mitigate risk, and streamline security operations.
In July 2024, Exabeam merged with LogRhythm, a cybersecurity firm specializing in SIEM, log management, network monitoring, user behavior, and security analytics since 2002, under the Exabeam brand. Exabeam’s cutting-edge AI technology, combined with LogRhythm’s unparalleled data integrity, created a unique platform capable of combating the most complex threats in any form factor chosen by clients (e.g., cloud-based, self-managing/on-premise, or augmented hybrid).
Exabeam New-Scale Fusion
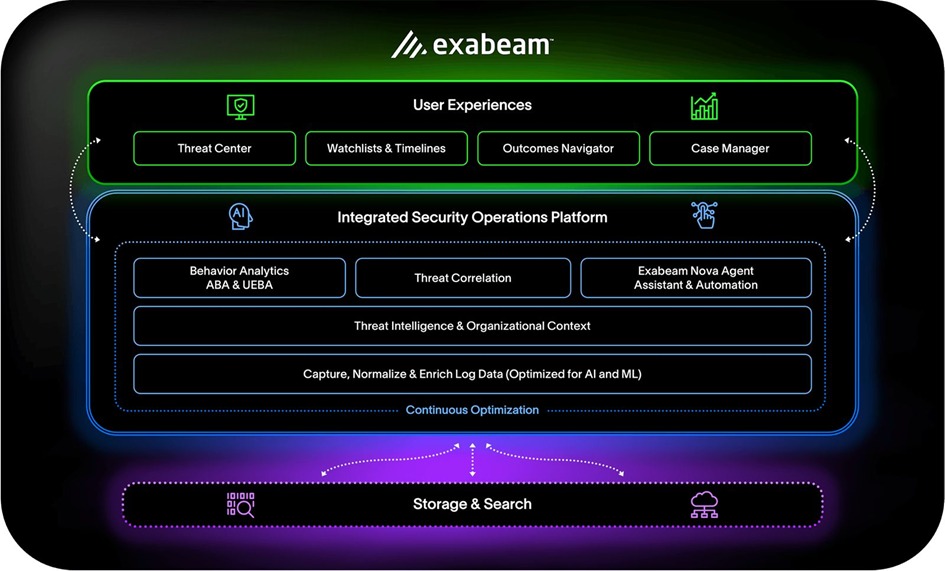
New-Scale Fusion brings together New-Scale SIEM and New-Scale Analytics solutions in a single modular, cloud-based platform that leverages AI, behavioral analytics, and automation in security operations workflows. Detect, investigate, and respond to threats faster.
Exabeam New-Scale SIEM
Exabeam New-Scale SIEM is a cloud-native SIEM solution that enables the collection, searching, and analysis of high-volume security data at cloud scale. It helps security teams investigate threats faster and respond to incidents more effectively by searching terabytes of data in seconds. It supports advanced queries as well as natural language search.
The central Threat Center workspace brings together alarms, incidents, detections, and watchlists in a single location. It automates threat prioritization, triage, and evidence gathering processes, enabling end-to-end management of detection, investigation, and response (TDIR) processes.
Exabeam Nova AI agents help automate routine or complex tasks in security operations, such as generating case summaries and classifying threats.
This reduces the manual workload for analysts while speeding up decision-making and intervention processes.
New-Scale SIEM also offers over 7,000 ready-to-use log parsers, data normalization with the Common Information Model (CIM), integrated threat intelligence, custom dashboards and reporting, correlation rules, and AI-powered detection engineering capabilities. It enables centralized management of security data from on-premises and cloud environments.
Exabeam New-Scale Analytics
Exabeam New-Scale Analytics adds behavioral analytics and automation capabilities to existing SIEM or data lake infrastructures, enabling earlier detection of advanced threats. It analyzes log data, learns about the normal behavior of users and assets, and identifies unusual activity, helping to prioritize risks.
Machine learning-powered behavioral analysis and dynamic risk scoring reveal credential-based attacks, insider threats, and anomalous activity. Self-learning behavioral models adapt to changing environments, helping security teams focus on real risks.
Exabeam Nova AI agents support tasks such as analyzing detections, gathering contextual information, summarizing cases, and automating triage processes. This reduces the manual workload for analysts while accelerating threat investigation and response processes.
New-Scale Analytics also extends behavioral analytics to AI agents and other non-human identities with Agent Behavior Analytics (ABA). By monitoring the activities of AI agents, it helps identify unusual behavior and potential insider risks. It can be integrated into existing security architectures with hundreds of ready-to-use integrations without requiring changes to the existing SIEM infrastructure.
Exabeam Nova AI Agent
Strengthen Security Operations with AI Agents
Exabeam Nova consists of AI agents that automate routine and advanced security operation processes. It helps security teams reduce manual workload, enabling them to analyze threats faster and focus on critical risks.
Nova agents automatically generate case summaries, classify threats, and identify high-priority assets in seconds using Global Search.
This allows security teams to speed up investigation processes, reduce alarm volume, and respond to threats more quickly.
Exabeam Outcomes Navigator
Exabeam Outcomes Navigator is a New-Scale Fusion component that helps measure the effectiveness of security programs and reveal gaps in security coverage. It enables real-time assessment of current security coverage by mapping collected data and existing configurations against strategic security use cases and accepted compliance frameworks.
MITRE ATT&CK® helps assess the current scope, identify gaps, and prioritize areas for improvement by aligning with OWASP Agentic Top 10 and various compliance frameworks. It reveals gaps at the data, configuration, or detection level by monitoring the security scope from data sources to active detection rules.
Exabeam Nova Advisor Agent, included in Outcomes Navigator, generates reports that compare the scope of use cases to similar organizations and track progress over time. This makes the impact of security investments more measurable and provides reportable outcomes for managers, auditors, and other stakeholders.
It also analyzes log quality, data parsing, and the effectiveness of detection rules, providing improvement recommendations to security teams. By including AI agent activity, it helps organizations assess their preparedness for security risks in next-generation work environments consisting of both human users and AI agents.
NetMon
NetMon is a network monitoring and analytics solution that enables organizations to monitor network traffic in real time and gain comprehensive visibility into network activity within LogRhythm or Exabeam New-Scale Security Operations Platform environments.
By analyzing communication and traffic on the network, it helps security teams detect suspicious activity, anomalies, and potential threats more quickly. Detailed visibility into network data makes it easier to investigate incidents and identify the source of threats.
NetMon combines data from network traffic with security operations to provide analysts with the context they need to understand who, what, where, and when events occurred. This contributes to faster and more effective threat detection and incident investigation processes.
Integrated with LogRhythm and New-Scale platforms, NetMon helps organizations more effectively monitor network-wide security risks by making network visibility a part of centralized security operations.
LogRhythm SIEM
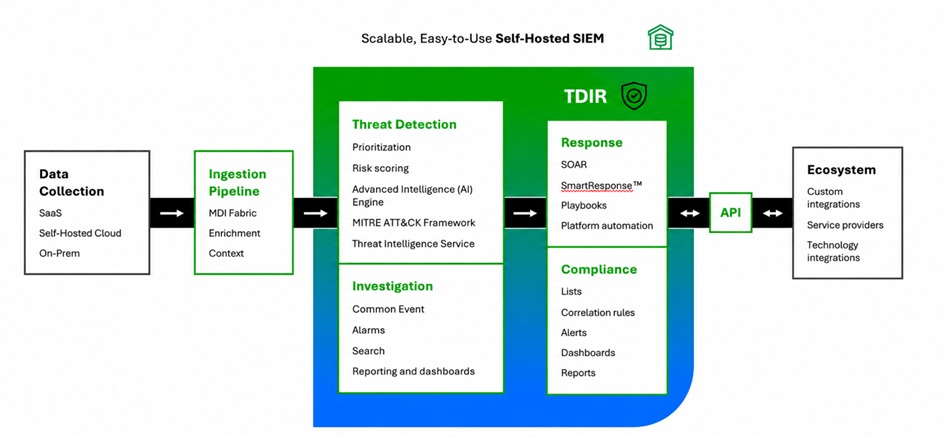
LogRhythm SIEM is a comprehensive security information and event management solution that can be deployed on-premises for organizations seeking complete control over their security environment. By combining centralized log management, threat detection, and security analytics capabilities, it helps organizations manage their security operations more effectively.
Thanks to its advanced analytics and precise threat detection capabilities, it continuously analyzes security data to identify suspicious activity and potential threats. By correlating security data from various sources in a central location, it allows analysts to assess events more quickly.
Automation and integrated threat intelligence help prioritize identified threats, accelerate investigation processes, and enable more effective incident response. This reduces the manual workload for SOC teams, making detection, investigation, and response processes more efficient.
Thanks to on-premises architecture, organizations can maintain control over their security data and infrastructure within their own environment, derive more value from existing security investments, and manage security operations according to their own requirements.
LogRhythm Intelligence™
LogRhythm Intelligence™ enhances LogRhythm SIEM's threat detection capabilities with artificial intelligence and behavioral analytics, helping to uncover risks that traditional SIEM approaches might miss.
By analyzing the normal behavior of users and assets, it identifies unusual activity. This helps in the earlier detection of compromised accounts, insider threats, and suspicious activity that can be hidden behind normal user behavior.
AI-powered analytics and behavioral insights enable security teams to focus on high-risk users and assets. By evaluating relationships and behavioral changes between different activities, it provides security analysts with the context they need when investigating threats.
LogRhythm Intelligence™, integrated with LogRhythm SIEM, provides additional behavioral visibility into existing security operations, helping to prioritize, investigate, and respond to threats more quickly.
LogRhythm NetMon
NetMon is a network monitoring and analytics solution that enables organizations to monitor network traffic in real time and gain comprehensive visibility into network activity within LogRhythm SIEM or Exabeam New-Scale Security Operations Platform environments.
By analyzing network traffic, it helps security teams identify suspicious activity, anomalies, and potential threats more quickly. Detailed information gleaned from network data provides analysts with the context they need when investigating security incidents.
Real-time network visibility allows security teams to more closely monitor communications and activity on the network. This makes it easier to identify the source of threats, understand the scope of incidents, and accelerate response processes.
NetMon, integrated with LogRhythm and New-Scale platforms, supports threat detection, investigation, and response processes by making network data part of centralized security operations.