
LogRhythm (Exabeam) NextGen OT SIEM
OT systems form the foundation of the infrastructure that powers our daily lives. The security of assets and data within the production and management networks of OT systems is critically important and can directly impact our lives. This critical infrastructure can be threatened by attacks originating from both OT environments and IT networks, as well as by attackers directly targeting OT environments.
As threat actors seek to exploit new vulnerabilities, inadequate security processes, or access weaknesses within organizations, it becomes increasingly important for security teams to secure the resilience and performance of critical infrastructure.
OT environments may need to integrate with IT networks, though not always directly. It’s crucial to be aware of the periodic processes of maintenance and support teams involved in OT environments, the risks associated with devices or data being moved from IT environments, and the dangers of remote access to the OT network. Using traditional techniques or narrow security technologies doesn’t always guarantee 100% security.
When using SIEM for IT environments, we monitor unauthorized access, user activity, network traffic events, or databases. So why not use a SIEM platform for monitoring OT environments as well? Continuous monitoring of OT environments, real-time detection of threats, and the accurate interpretation and analysis of genuine positive events using an OT security approach are crucial. An incident here could lead to consequences beyond simply disrupting operations or damaging reputation; it could result in vital losses.
Uni-Directional Collection
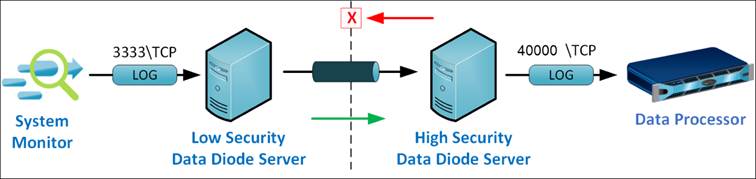
When monitoring OT environments, it’s crucial to ensure both visibility and security, and to guarantee secure one-way transmission of logs. LogRhythm (Exabeam) NextGen SIEM offers a suite of features that enable advanced monitoring and threat analysis for OT environments.
Specifically designed for collecting logs from OT environments, OT Collector ensures secure and one-way transmission of events to your SIEM on your IT network. Of course, SIEM for OT environments doesn’t just mean one-way log transmission.
Process Data Collection
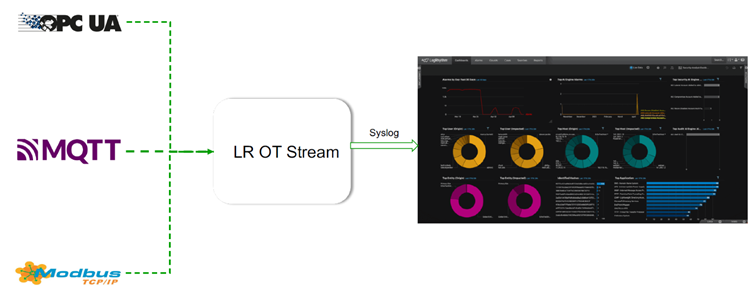
LogRhythm SIEM processes logs by understanding various OT protocols. It includes ready-to-use, predefined OT-specific correlation rules, and AI Engine Alarm rules run proactively.
For example, let’s consider a SCADA system . It can detect configuration changes in the SCADA system and automatically generate alarms, and thanks to its Case Management feature, it can automatically create a case for the relevant SCADA system.
In OT environments, it simplifies monitoring with dozens of OT dashboards based on incoming logs. LogRhythm NextGen SIEM ensures complete visibility and control of the IT/OT environment.
Thanks to integrated SOAR , you can instantly stop unauthorized and suspicious user activity. It includes continuously updated Dashboards, Playbooks, and AI Engine rules specific to industry (healthcare, energy, etc.) or various OT regulations for OT systems.
With LogRhythm SIEM , you’re always one step ahead, able to do more.